
Non-Human Identities Are Becoming a Security Blind Spot
Without visibility into their ownership, permissions, and activity, these identities can accumulate access and become difficult to govern.

Identity Sprawl
Service accounts, API connections, OAuth tokens, agents can create identities across disconnected systems. Without centralized visibility, security teams can struggle to determine what exists, where it operates, and what it can access.

Excessive Access
Non-human identities are often given broad permissions to keep automated workflows running. Over time, those permissions can exceed what the workflow actually requires, increasing the potential impact of misuse or compromise.

Unclear Ownership
Unlike employee identities, non-human identities may not have an obvious owner or lifecycle. When an identity outlives its application, workflow, or original purpose, unused access can remain active without clear accountability.

Invisible Activity
Traditional identity controls can confirm that a credential is valid without understanding the action it is being used to perform. That creates a gap between authorized identity and authorized behavior when automated systems access sensitive resources.


The NHI Security Gap Is Growing
Non-human identities already outnumber human identities across modern environments, while security teams continue to struggle with visibility, privilege, and control.
machine identities exist for every human identity. CyberArk found that machine identities outnumber human identities by 82 to 1.
of security leaders experienced a machine identity-related incident or breach. CyberArk found that half of surveyed security leaders reported a machine identity-related security incident or breach in the previous year.
of NHI incidents were linked to poor credential rotation. Astrix and Cloud Security Alliance found that lack of credential rotation was the most commonly reported cause of NHI-related security incidents.
of organizations have little or no visibility into third-party OAuth vendors. Astrix and Cloud Security Alliance found that 38% of organizations reported low or no visibility into third-party vendors connected through OAuth applications.
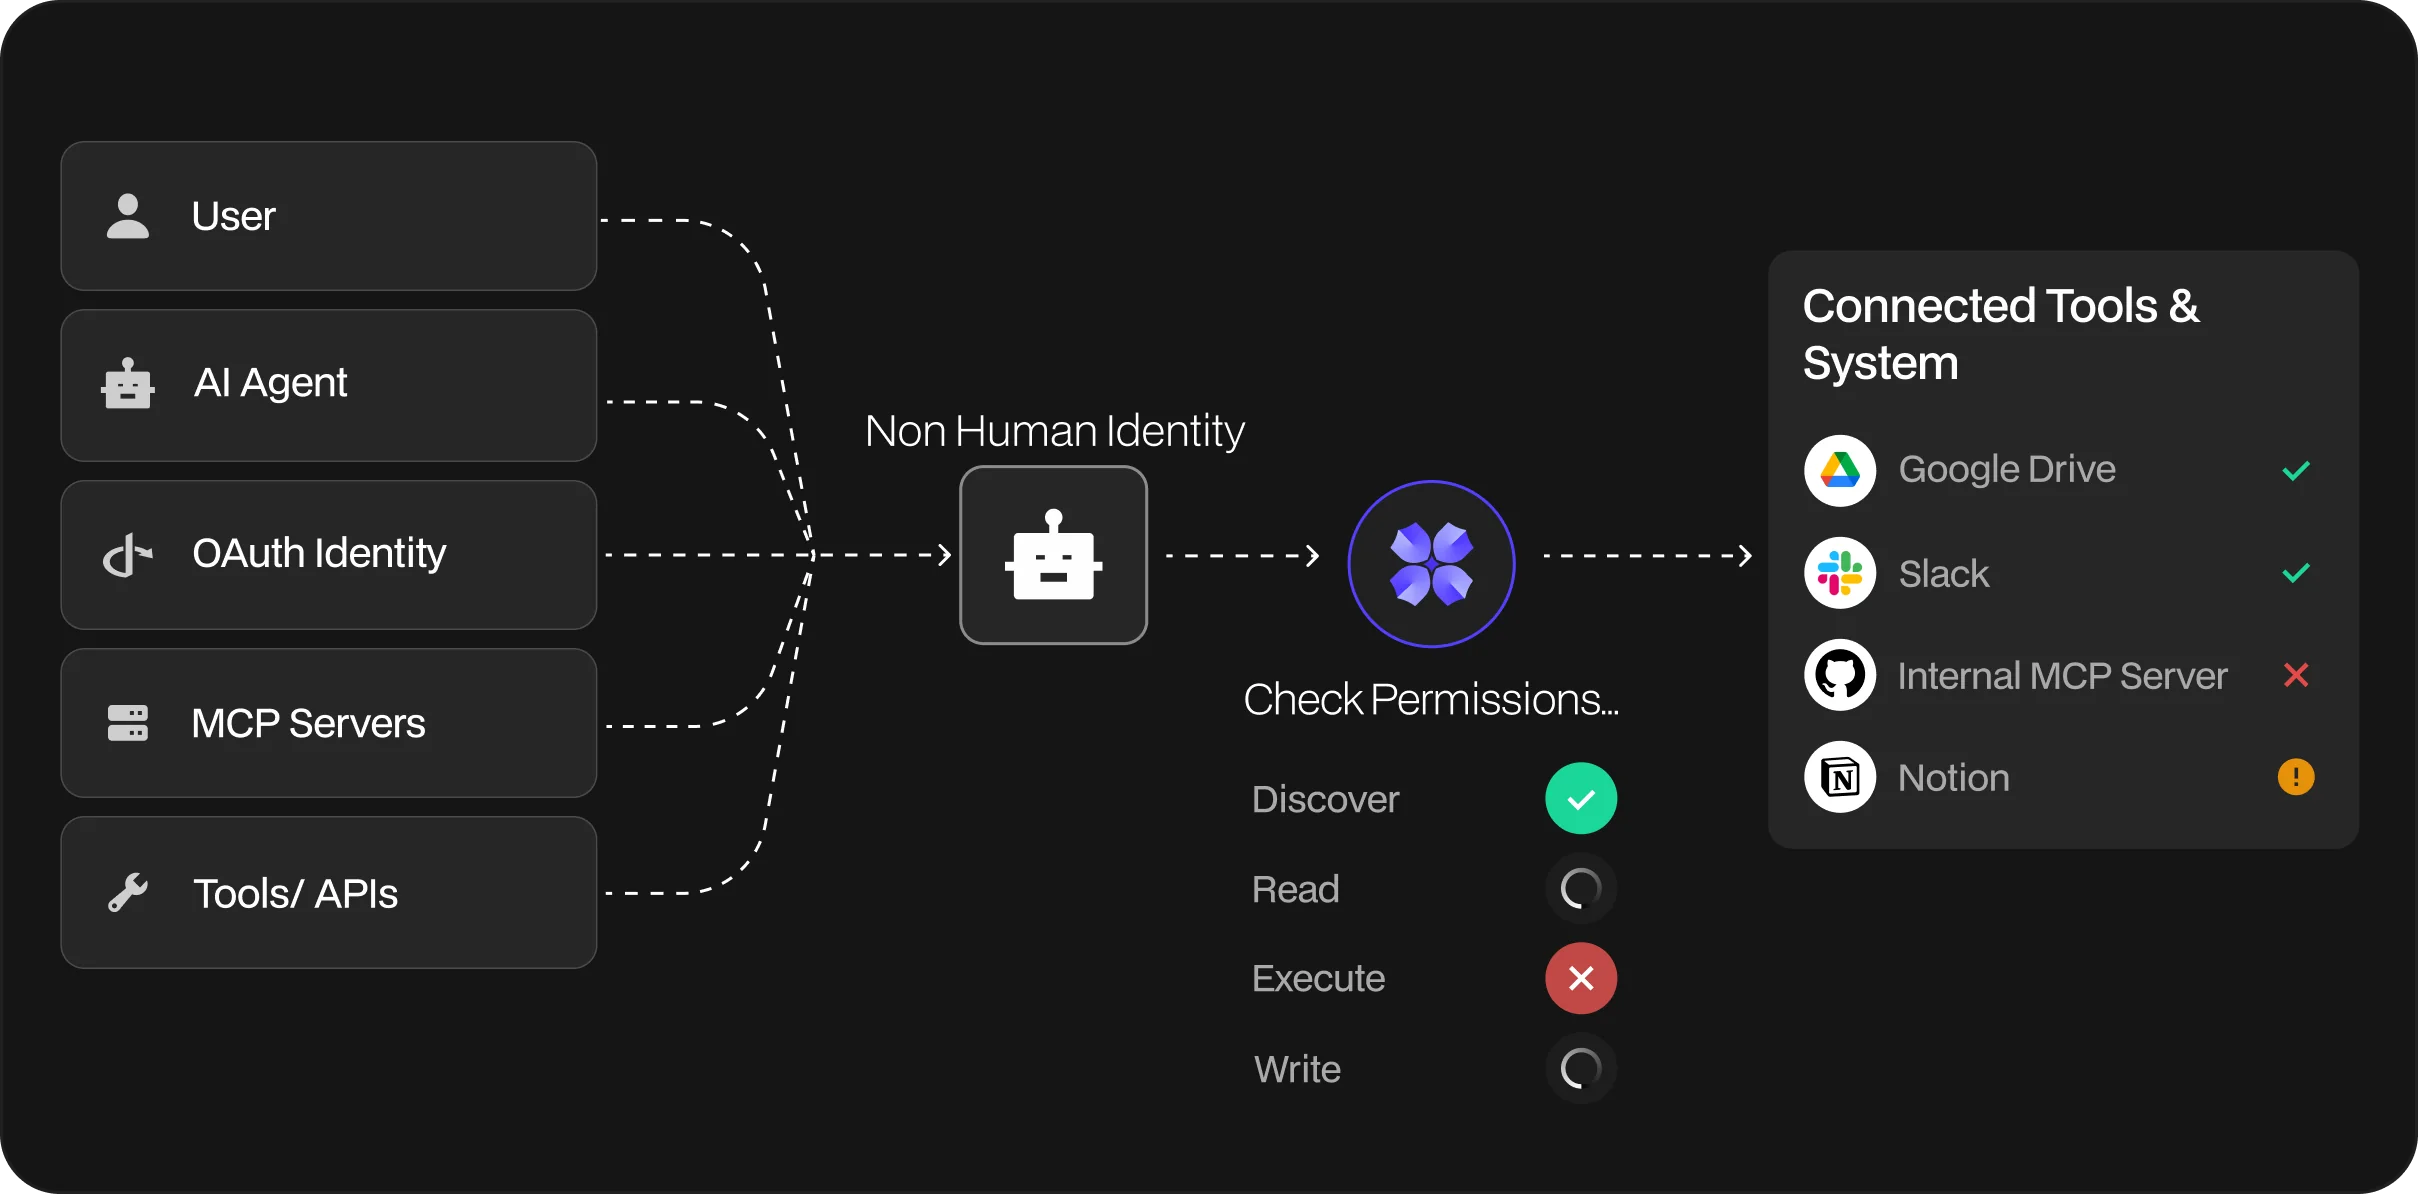
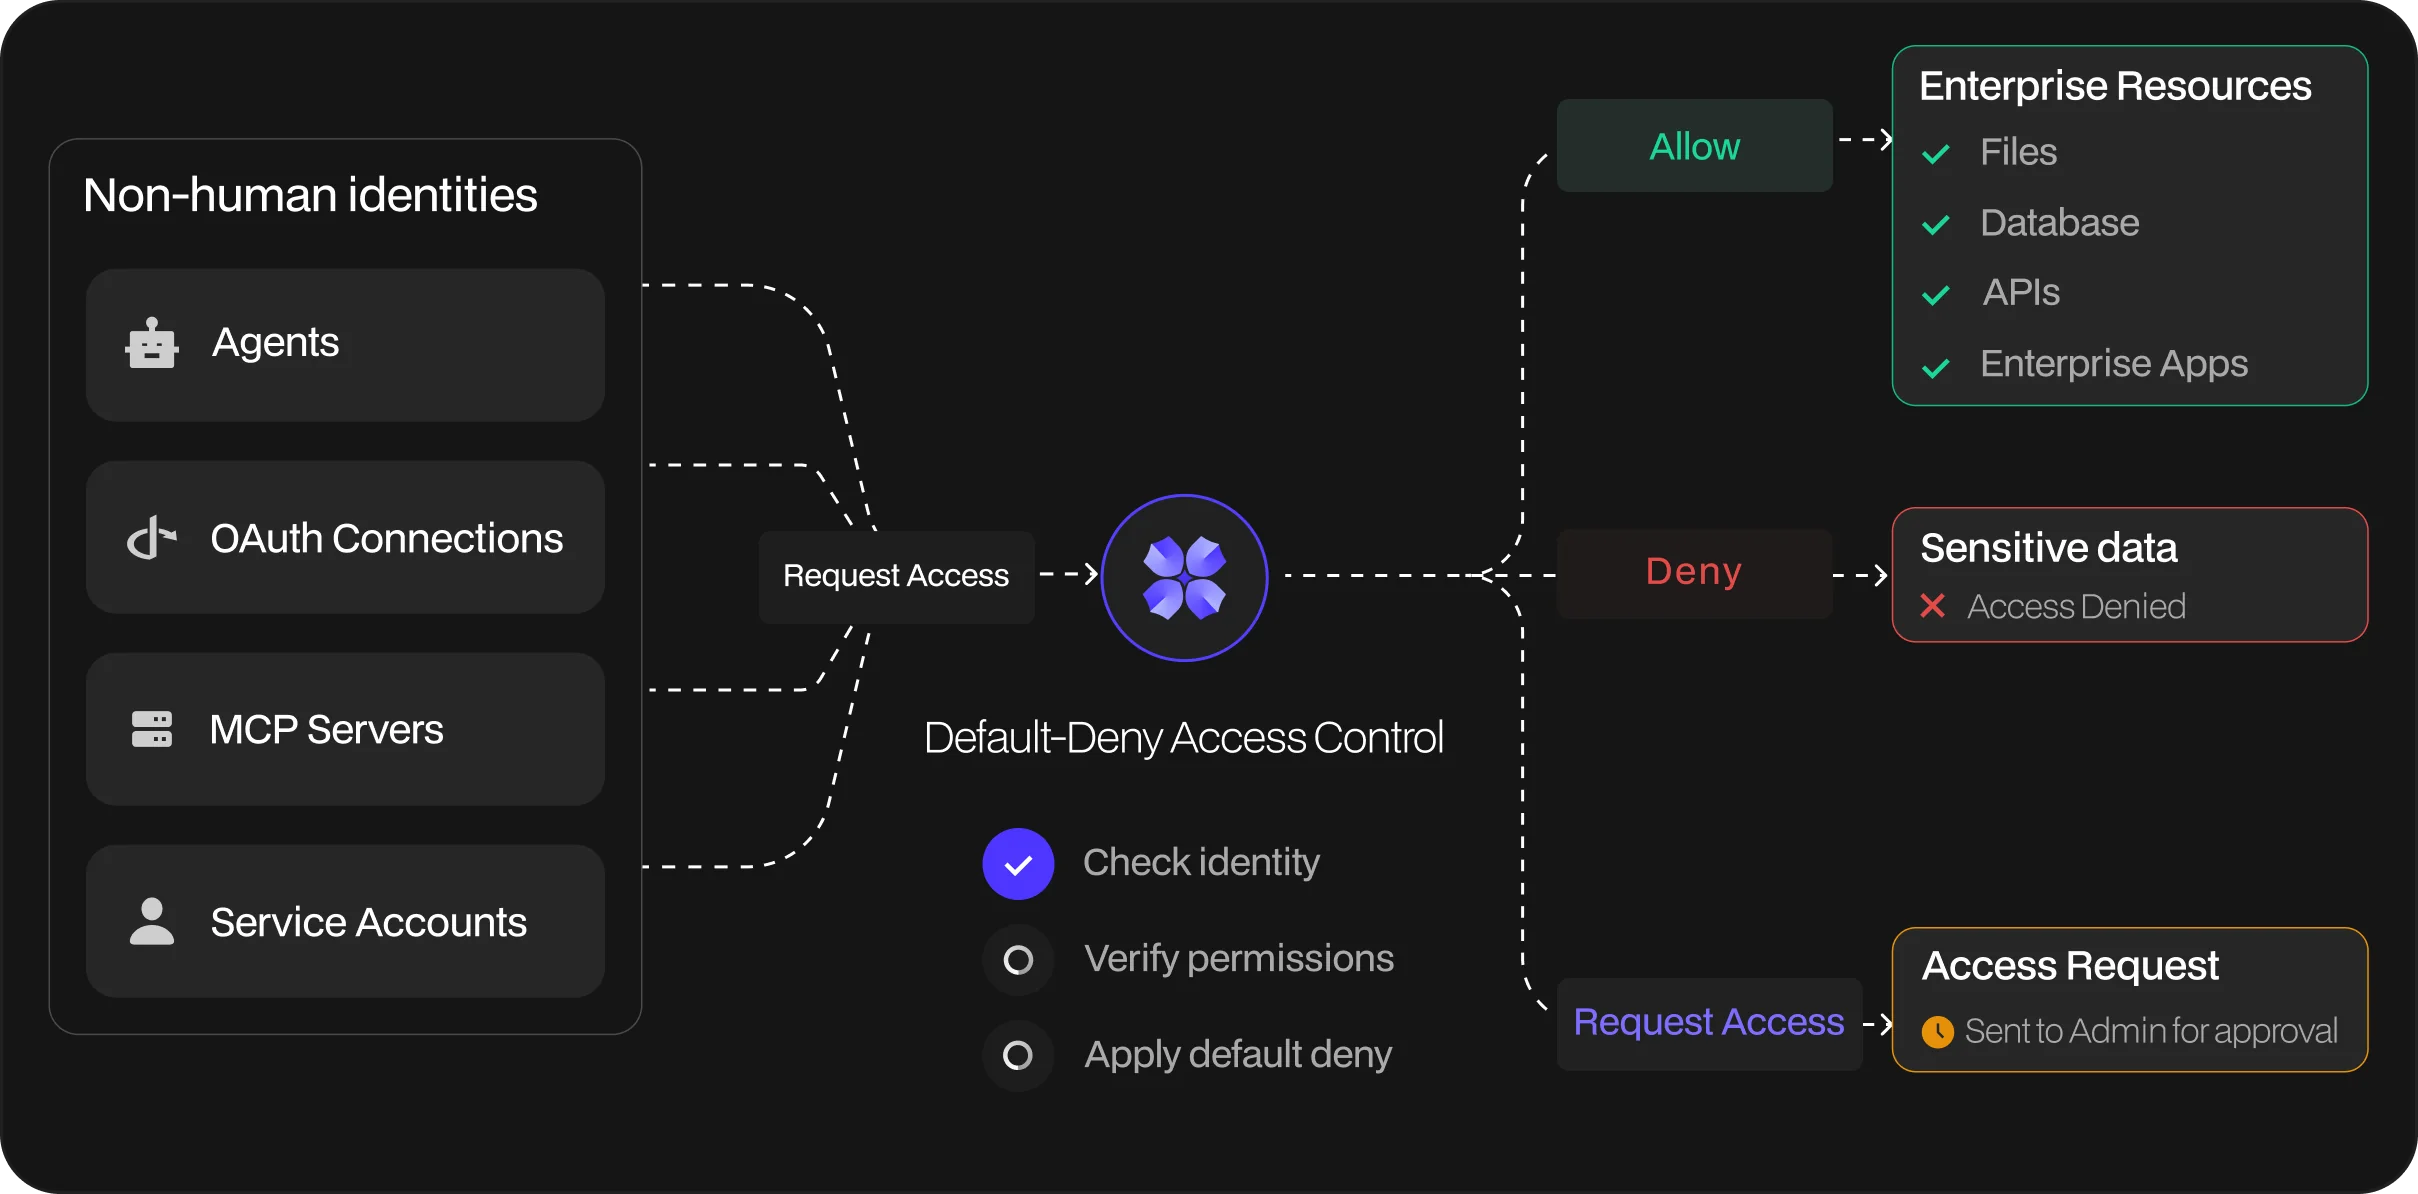
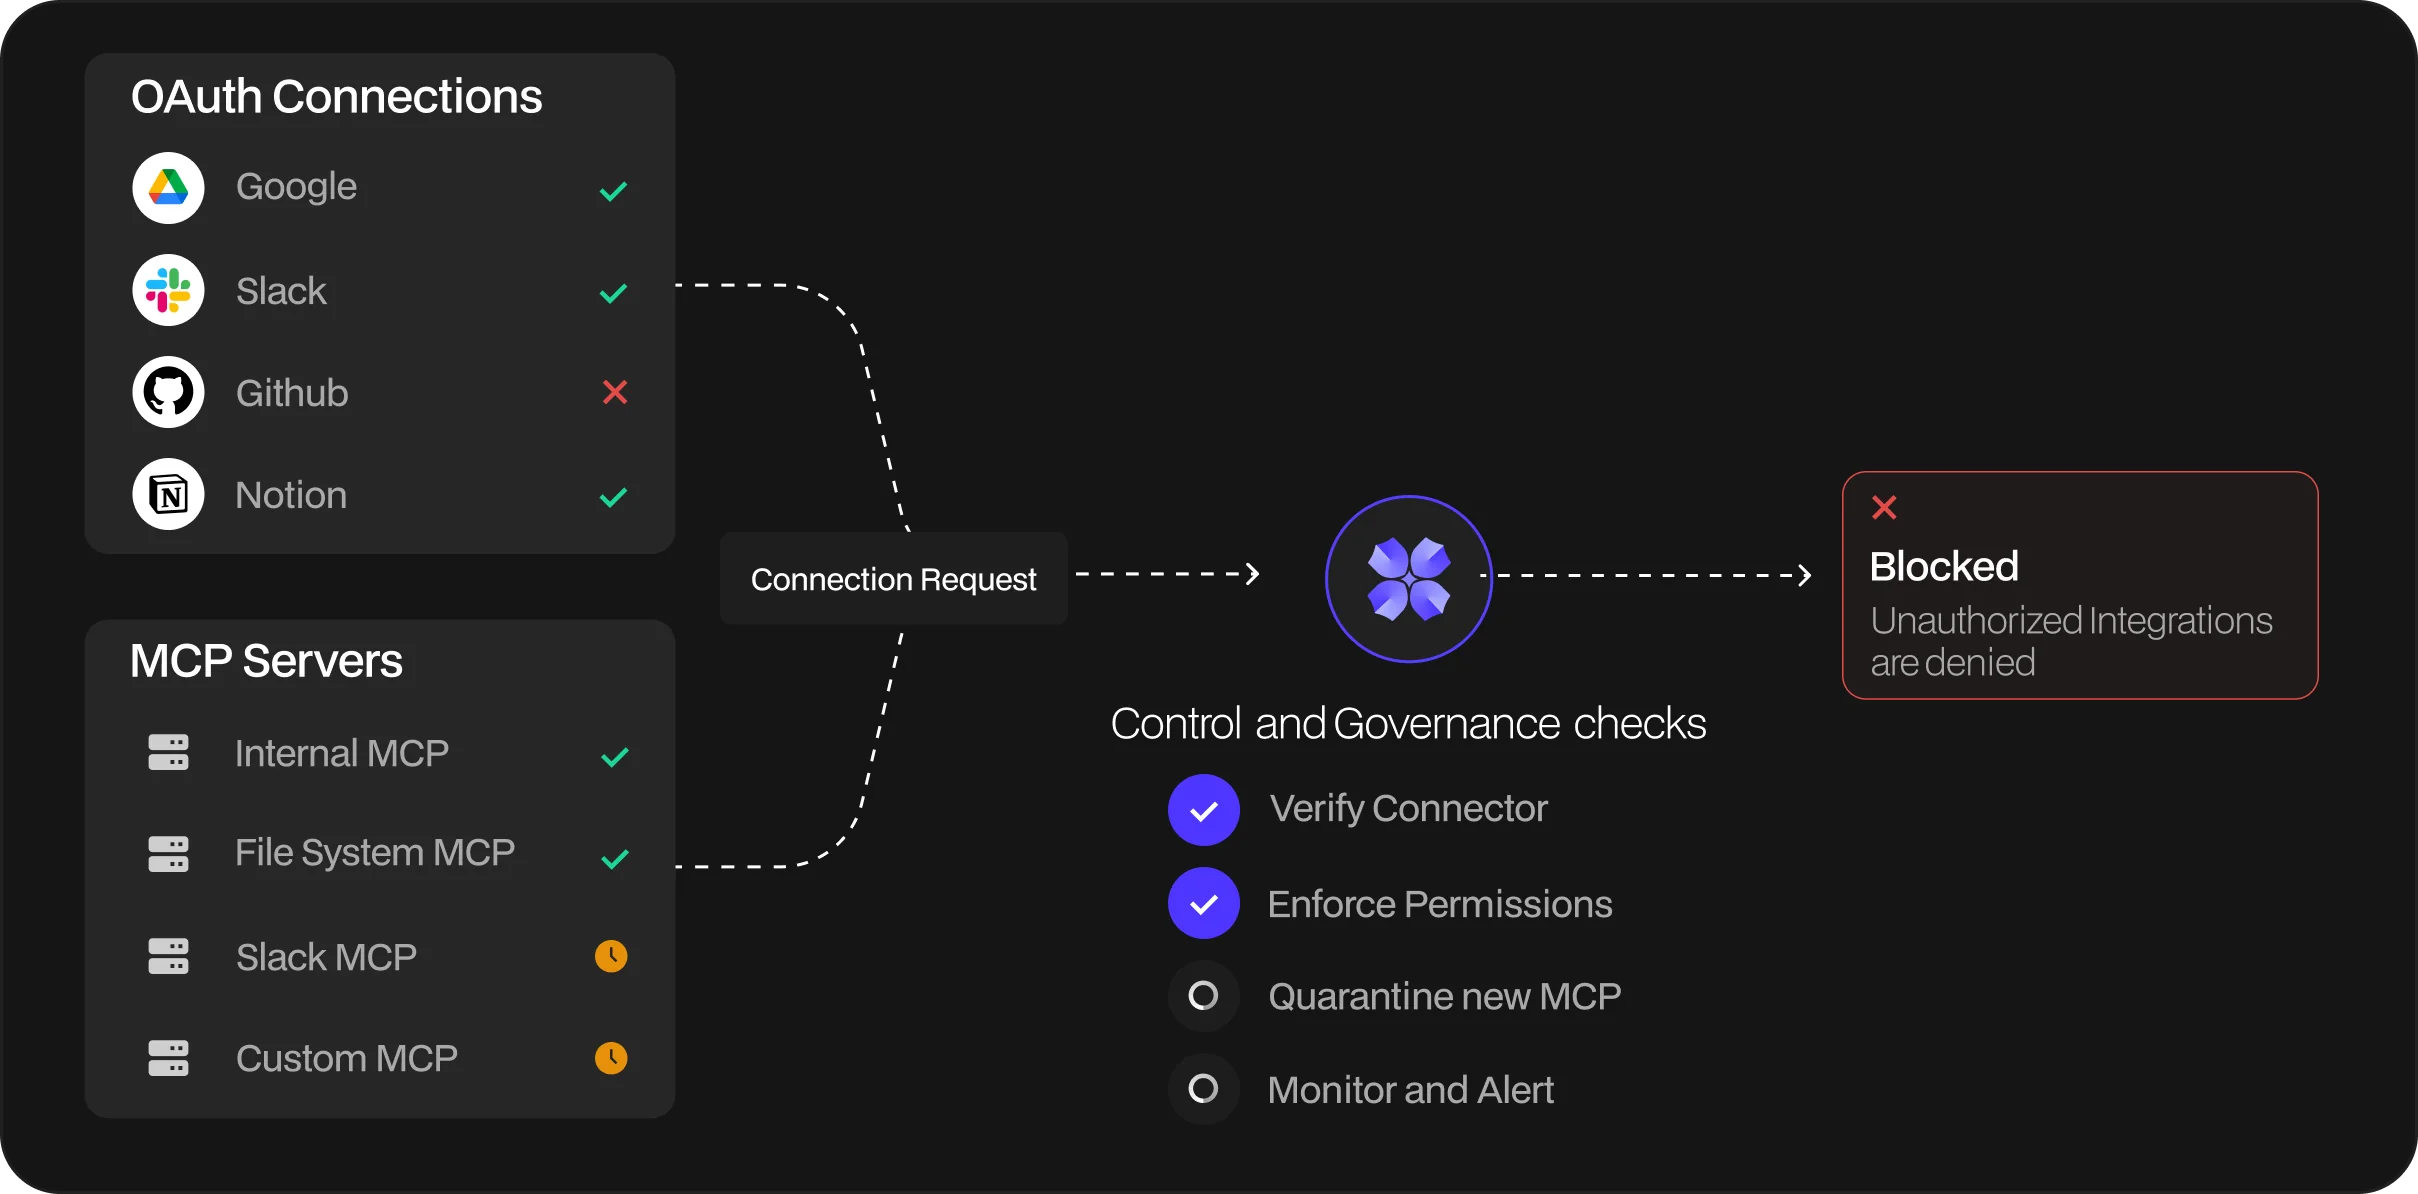
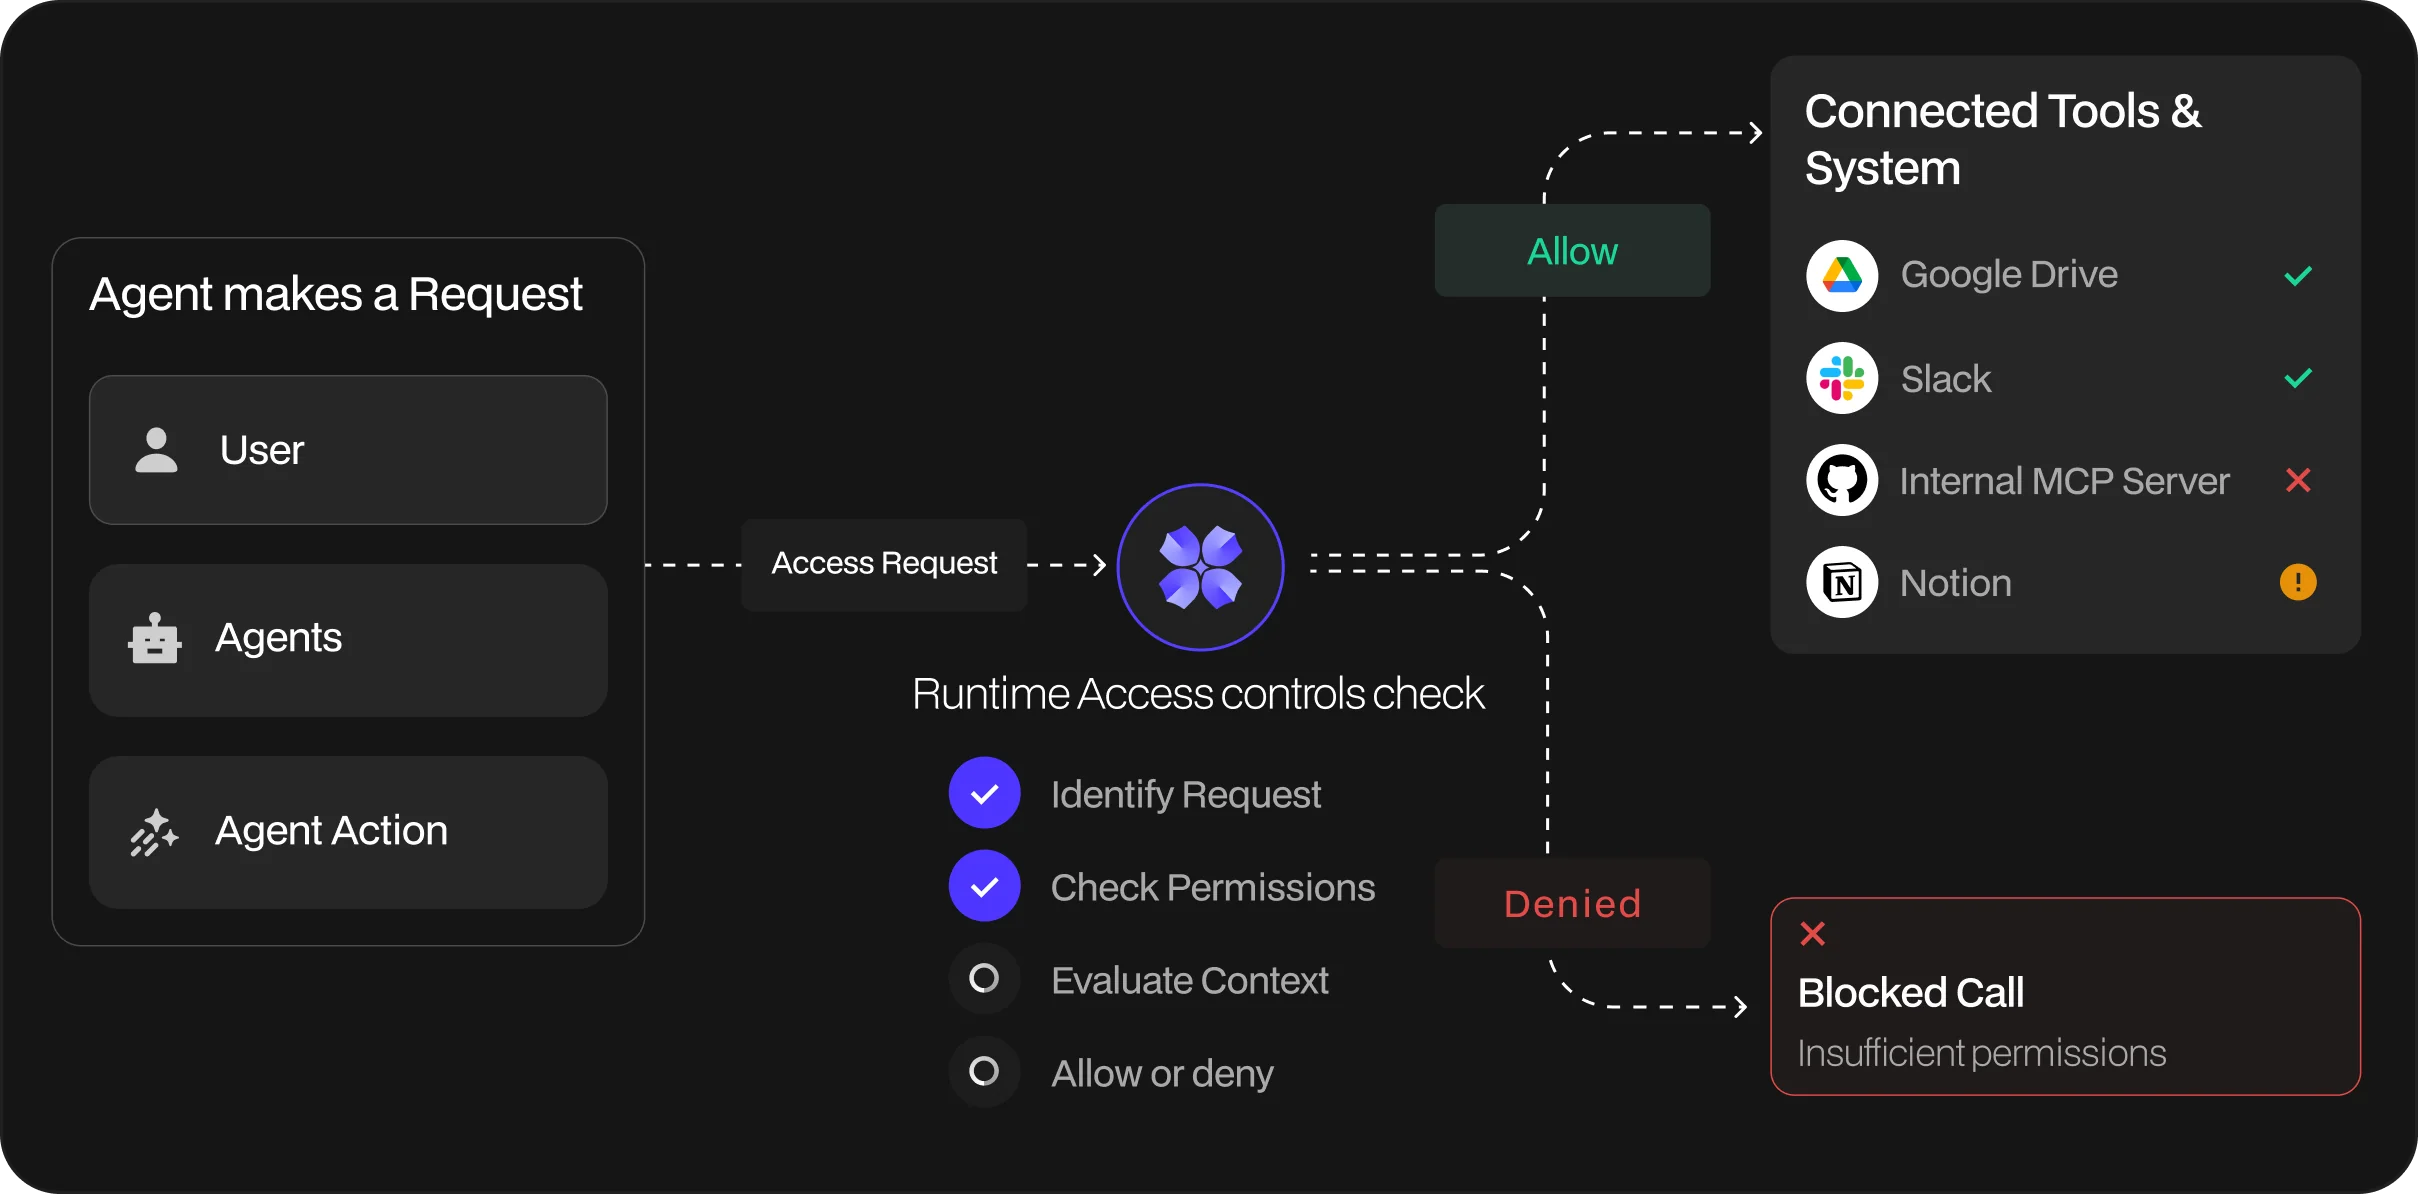
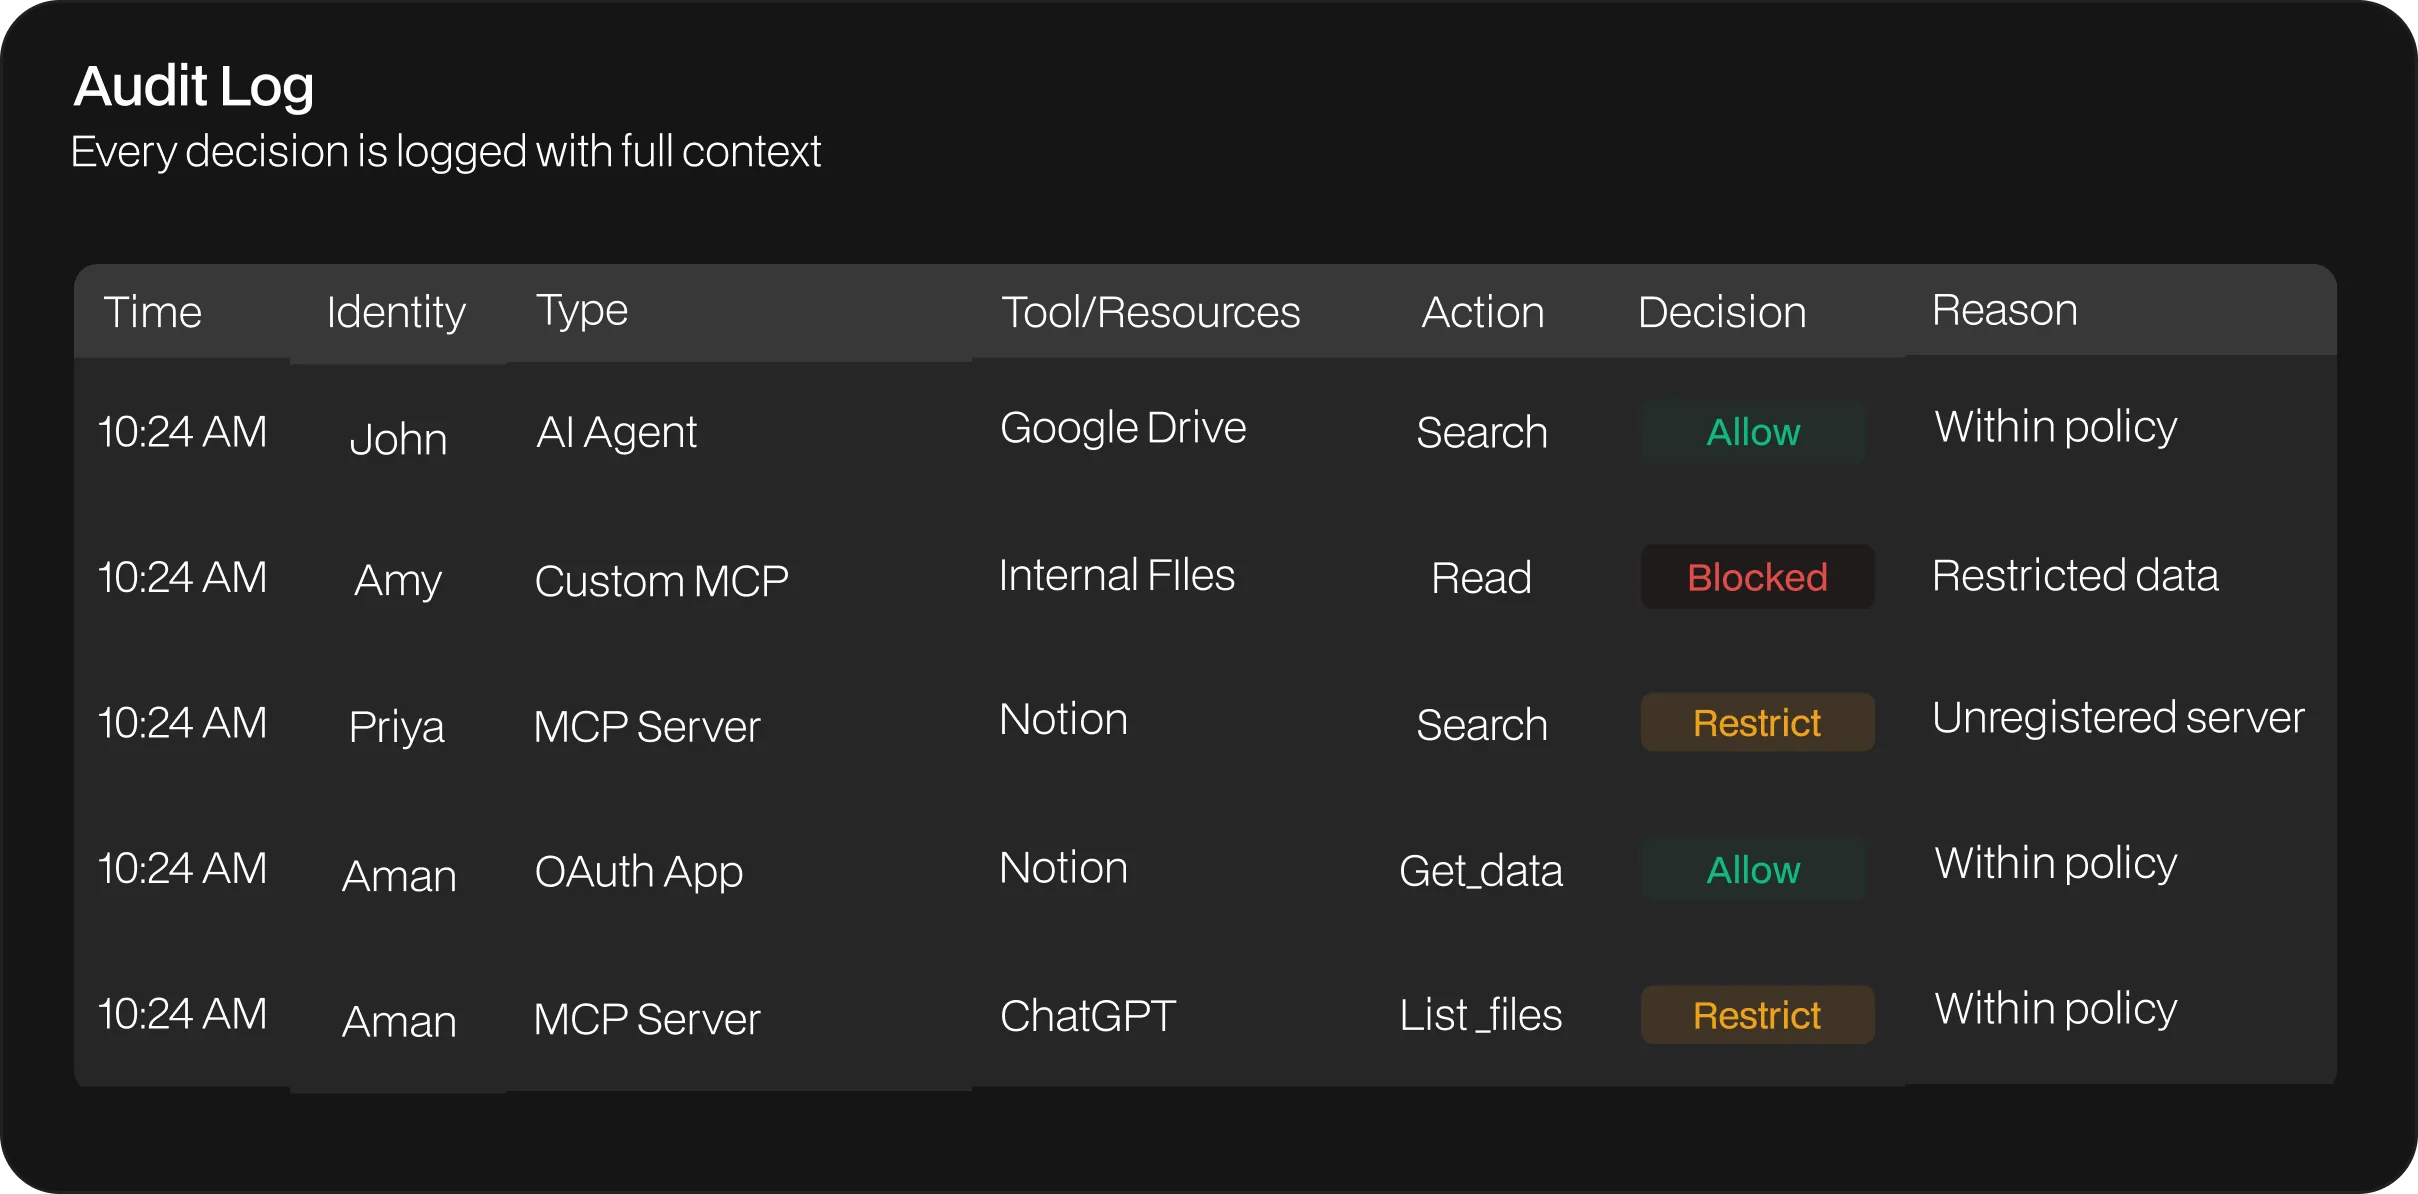
How LangProtect Secures Non-Human Identities
LangProtect brings identity, access, context, and runtime enforcement together so security teams can understand what non-human identities can access and control what they are allowed to do.
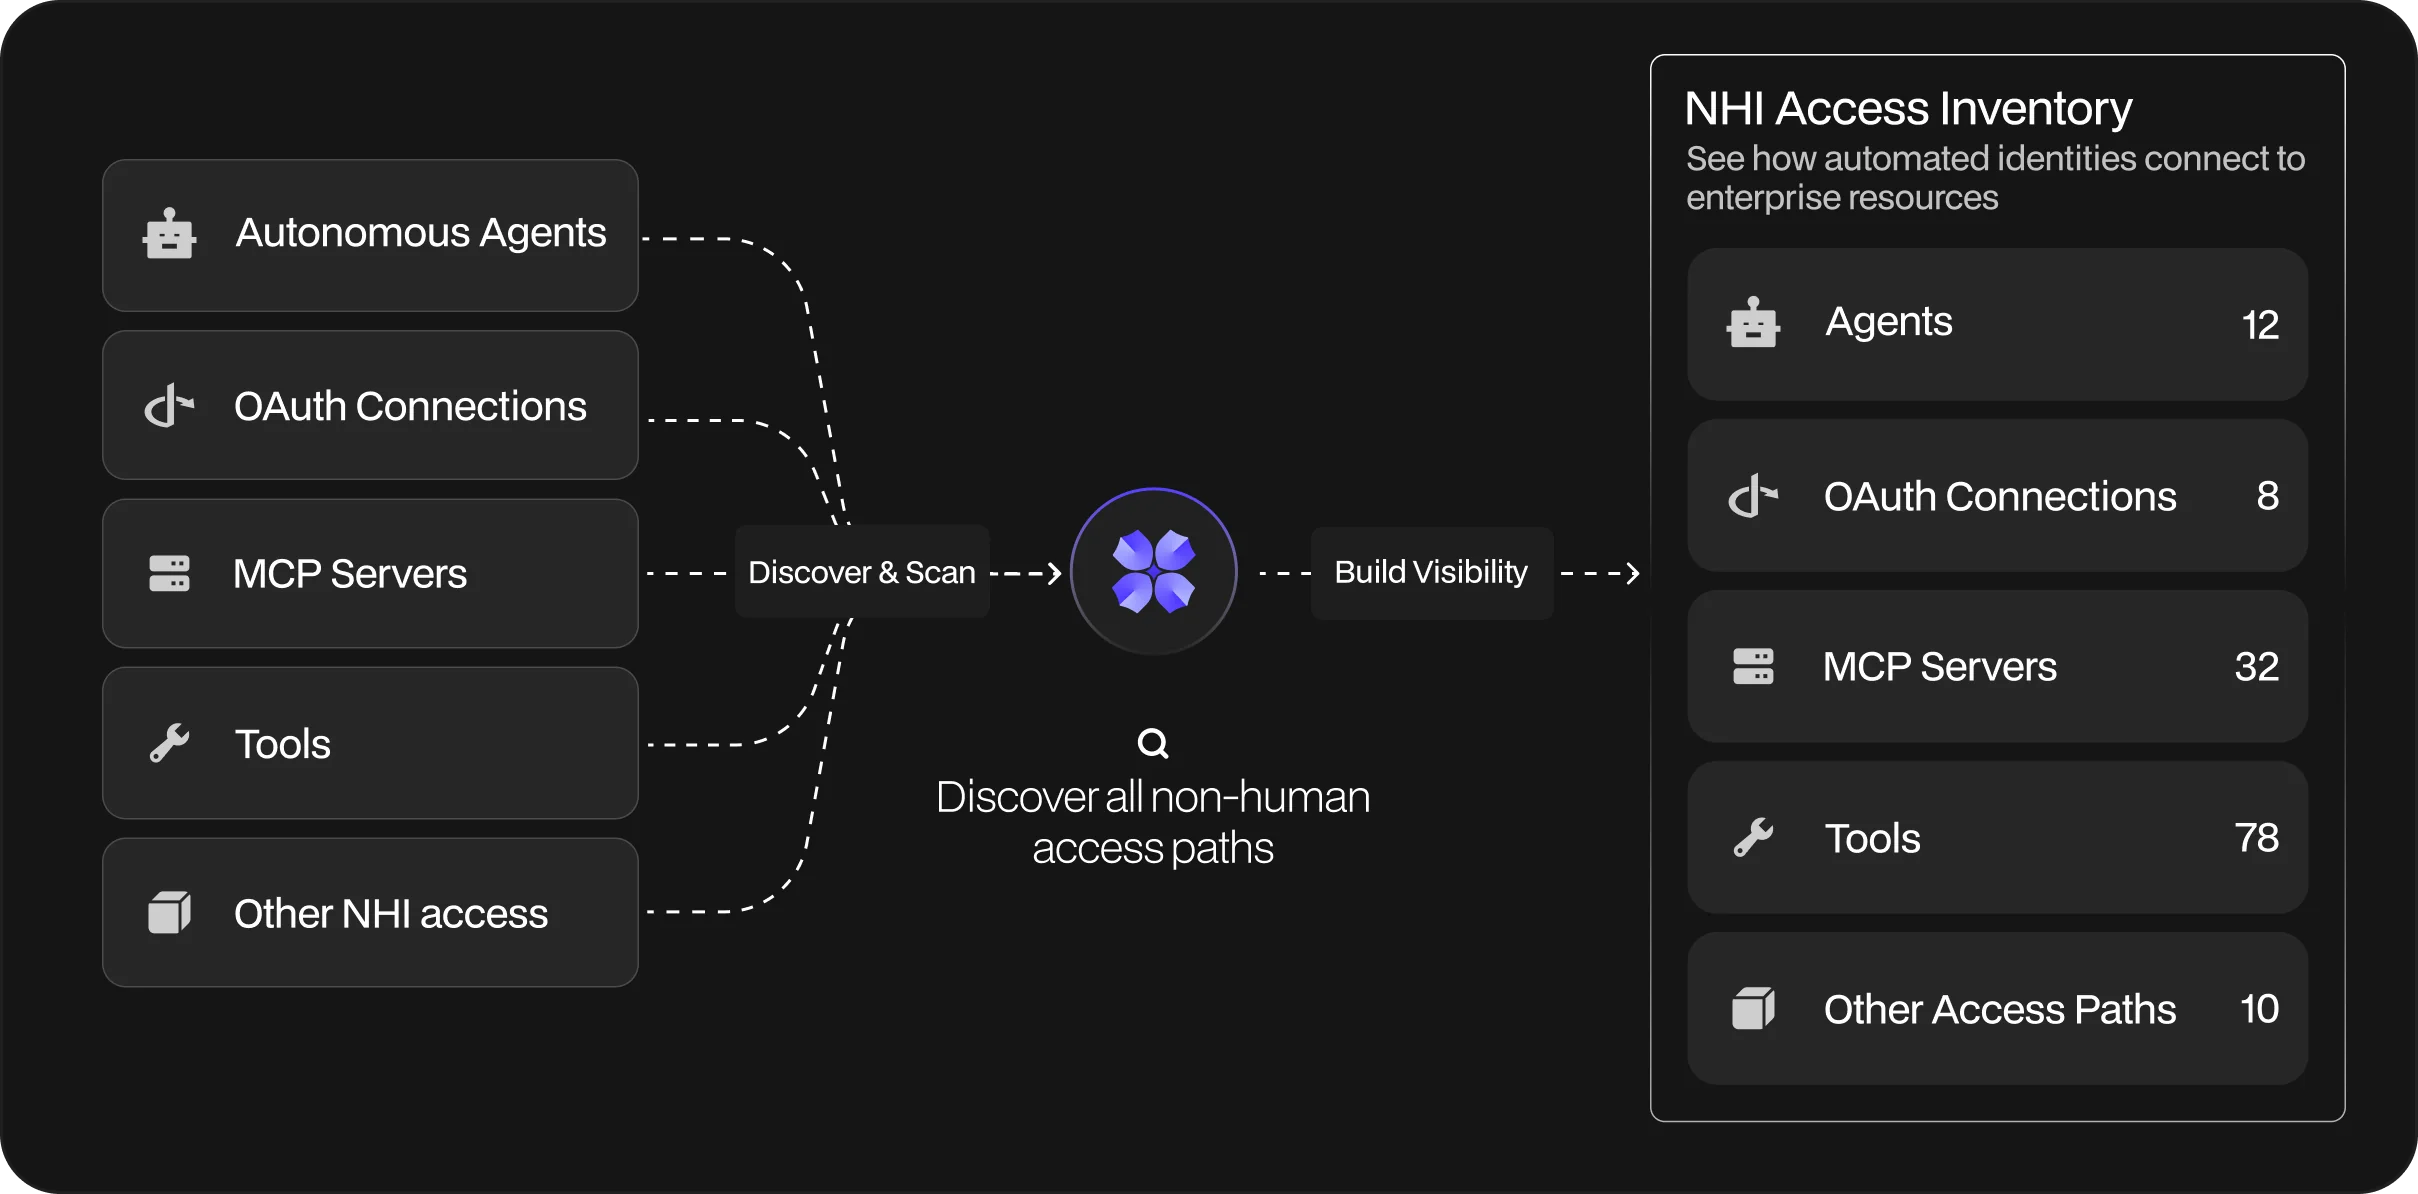
Identify autonomous agents, OAuth connections, MCP servers, tools, and other non-human access paths operating across your AI environment. Build visibility into how automated identities connect to enterprise resources.
Secure Non-Human Access Without Slowing Automation
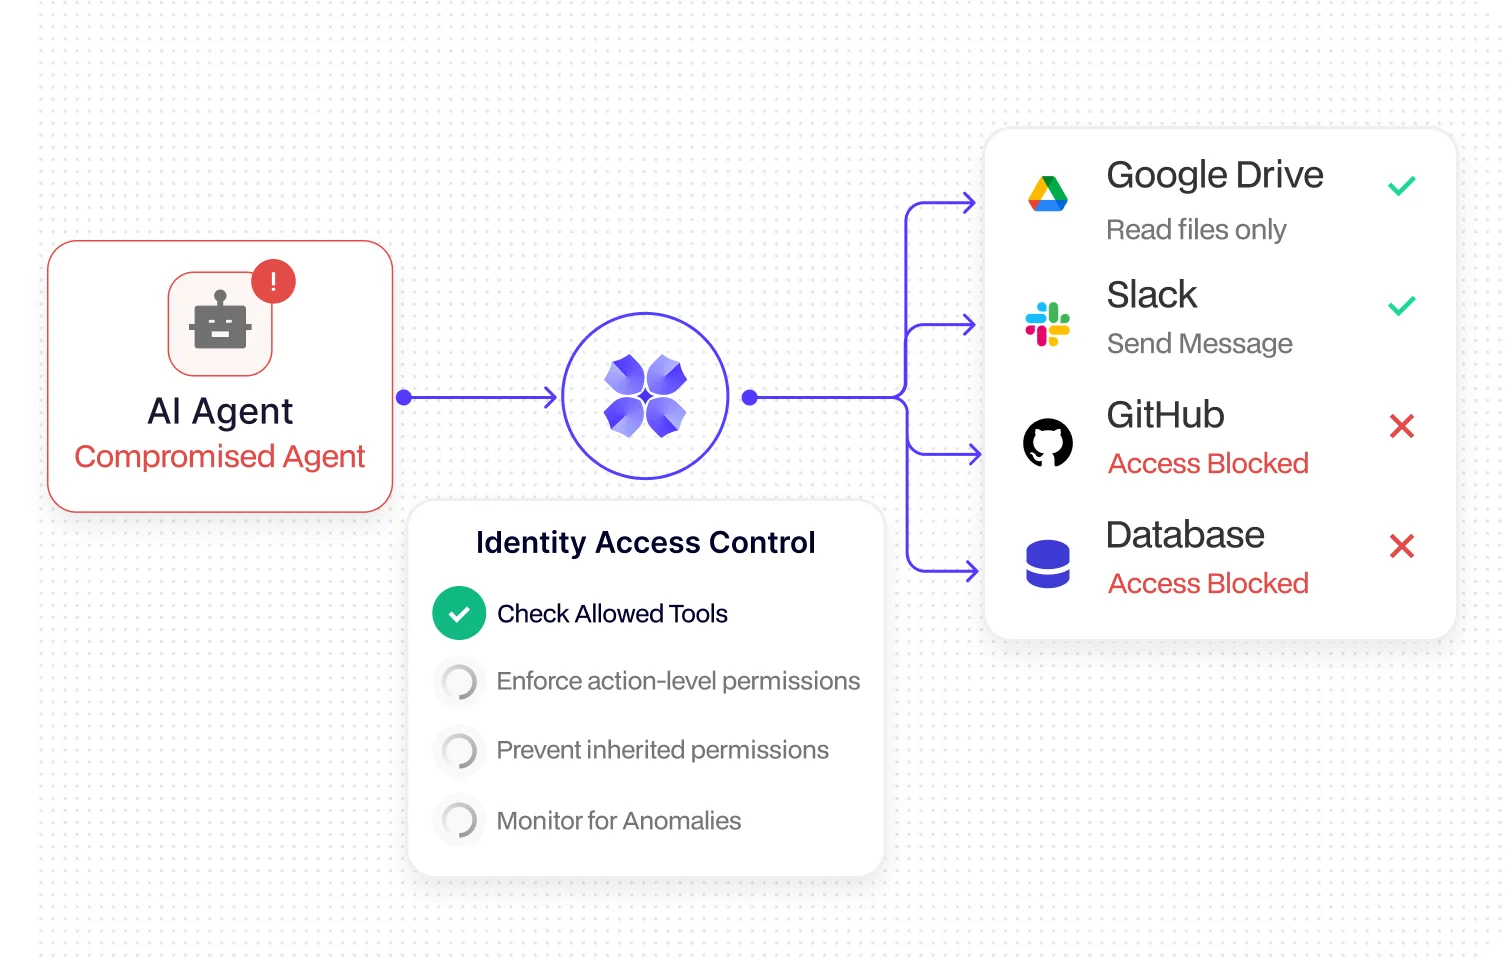
Reduce the Blast Radius of Compromised Identities
Limit non-human identities to the specific tools, resources, and actions they are authorized to use. Prevent broad credentials or inherited permissions from turning a single compromised identity into unrestricted enterprise access.
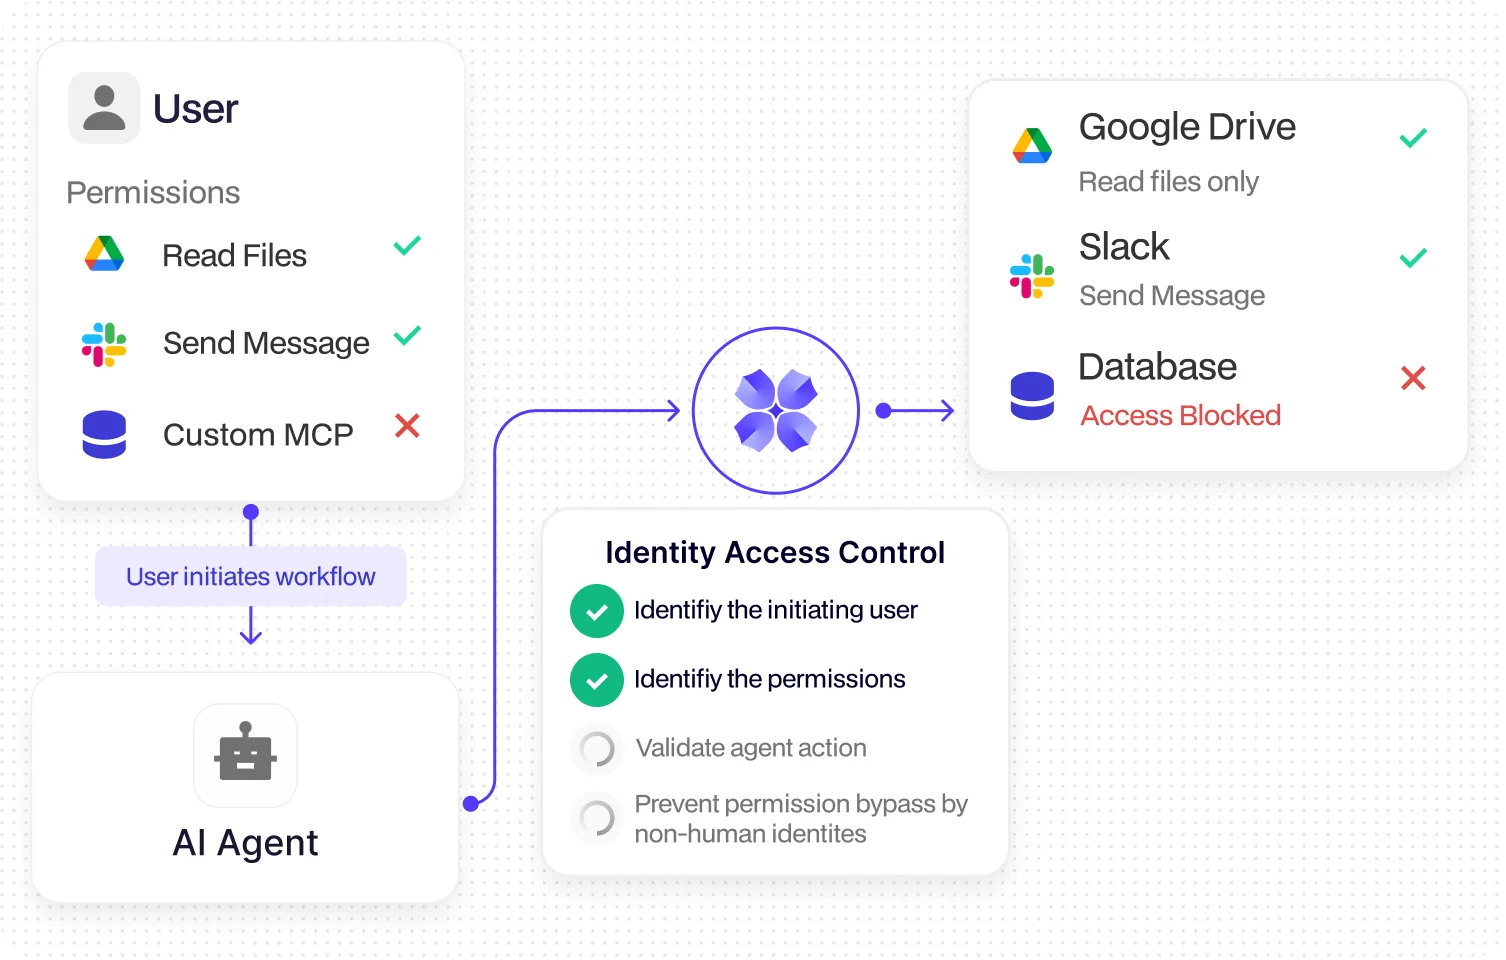
Keep Automated Access Aligned With Human Authorization
Tie agent actions to the permissions of the user initiating the workflow. Let automation operate at machine speed without allowing non-human identities to bypass the access boundaries applied to people.
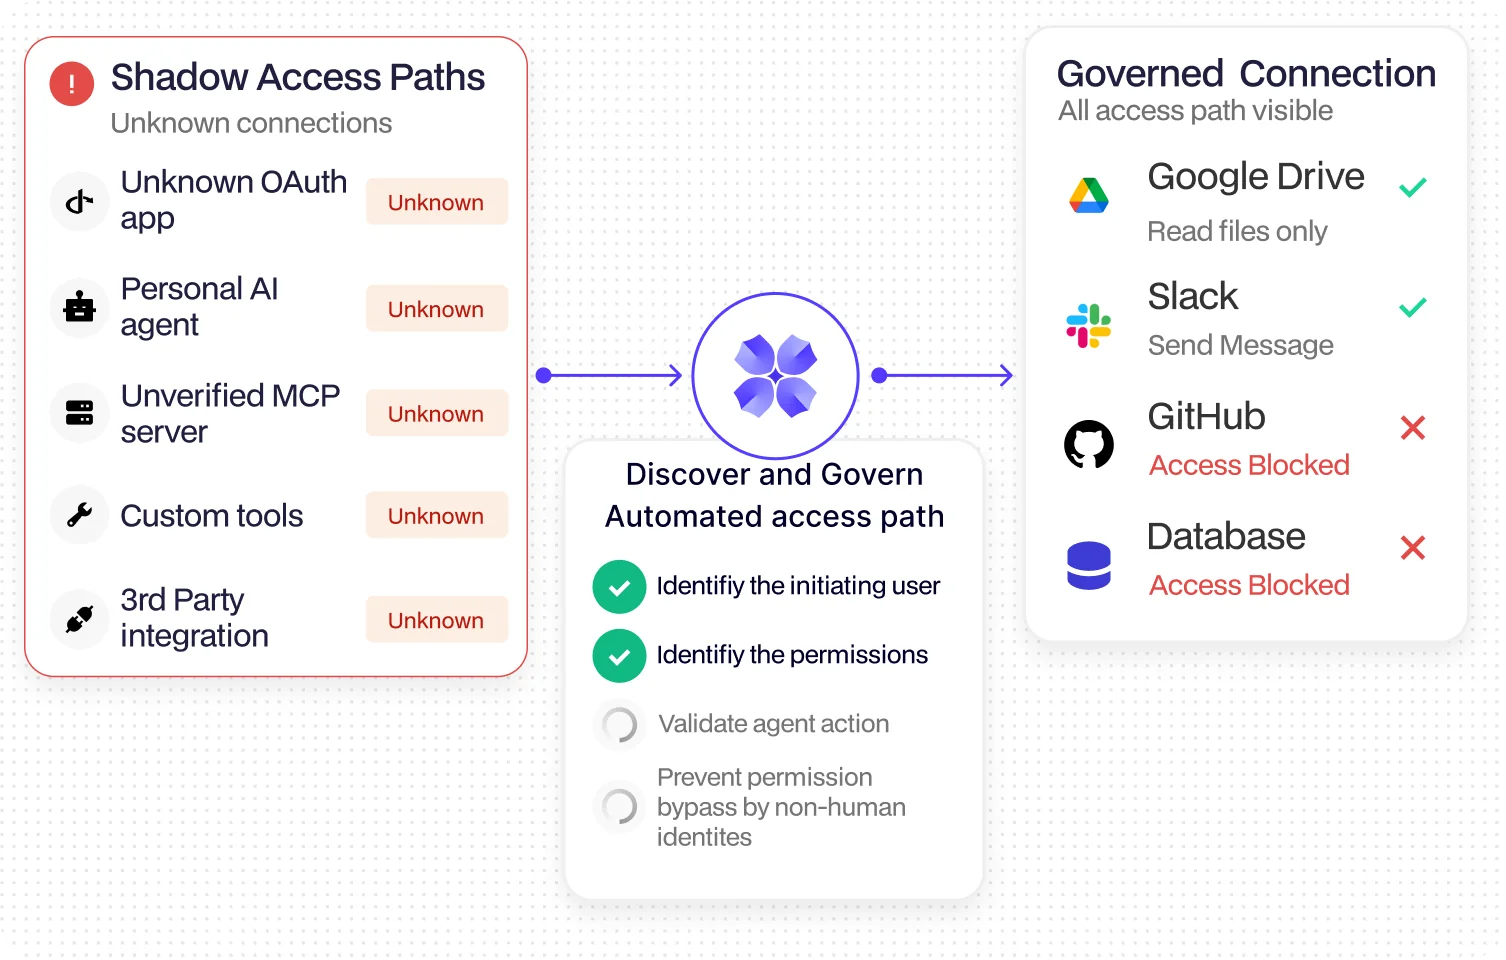
Bring Shadow Access Paths Under Control
Gain visibility into OAuth connections, MCP servers, agents, and other automated access paths that can otherwise remain outside traditional identity controls. Identify unknown connections and apply policy before they become persistent risks.
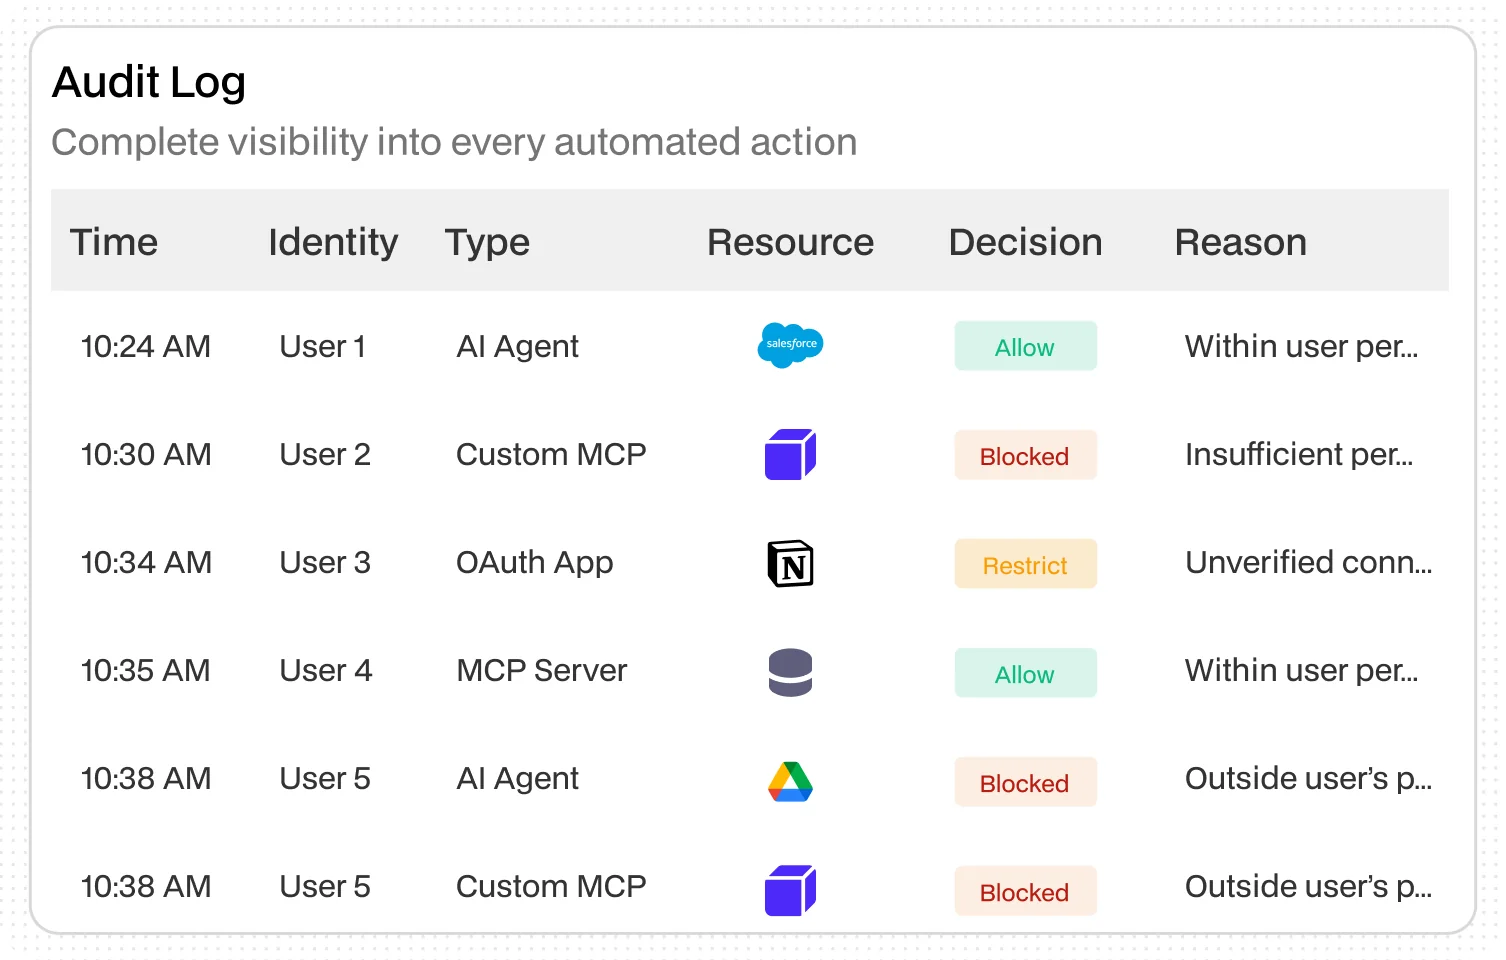
Make Every Automated Action Accountable
Connect identity, agent, tool, action, decision, and timestamp in a single audit trail. Give security teams the evidence needed to investigate activity and understand exactly how an automated identity interacted with enterprise systems.
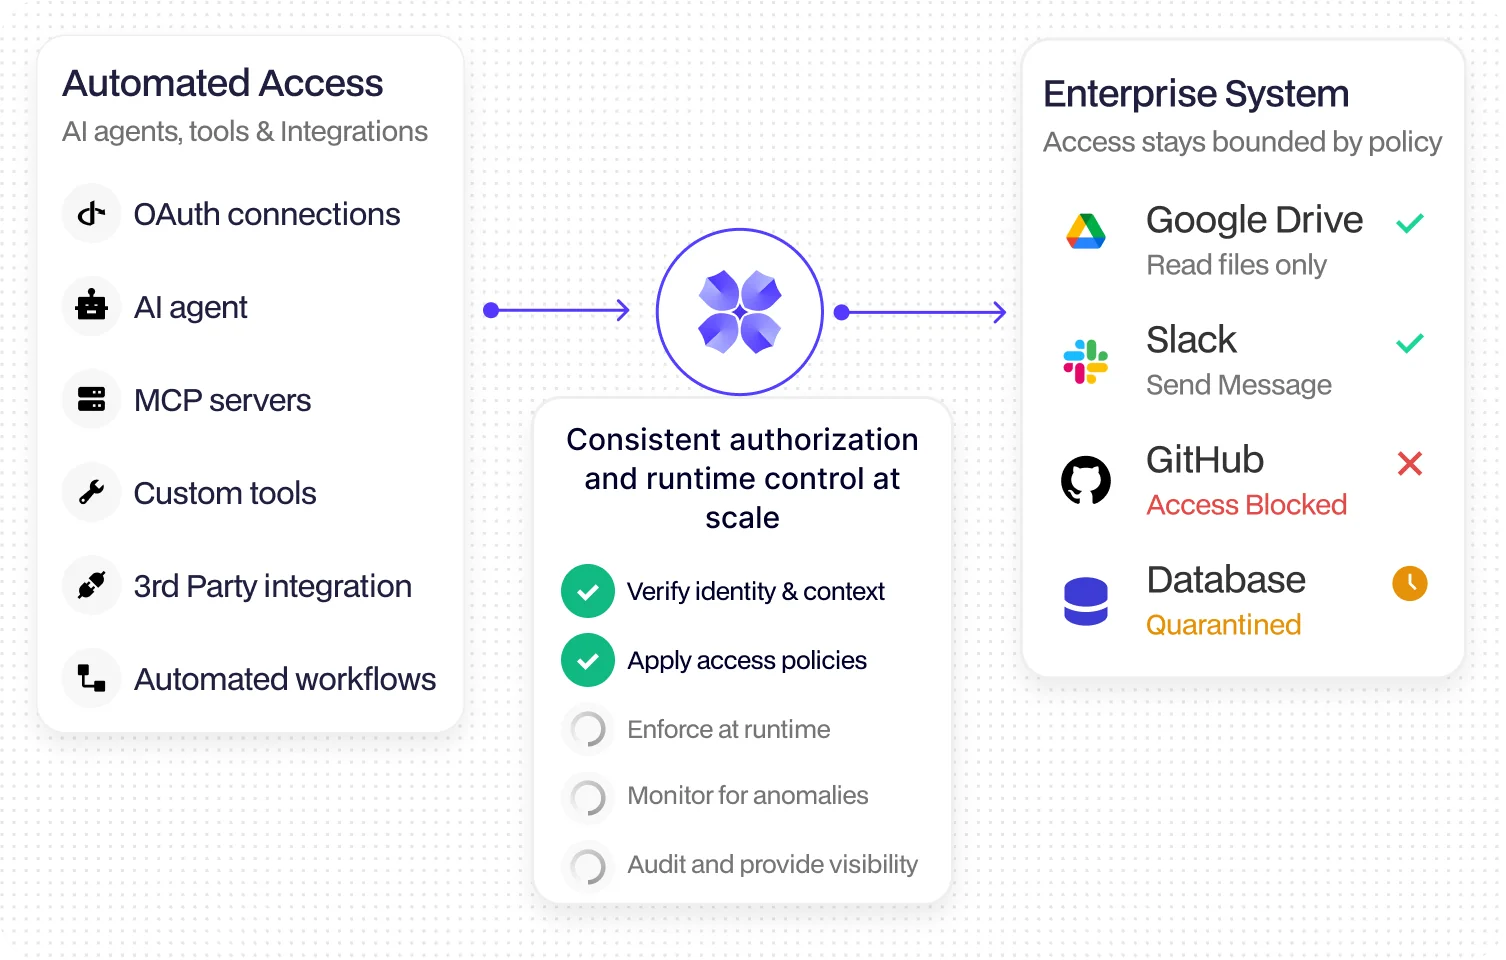
Scale Automation Without Expanding Uncontrolled Access
Apply consistent authorization and runtime controls as automated identities, AI agents, and connected tools multiply across the enterprise. Give teams room to automate while keeping access bounded by policy.
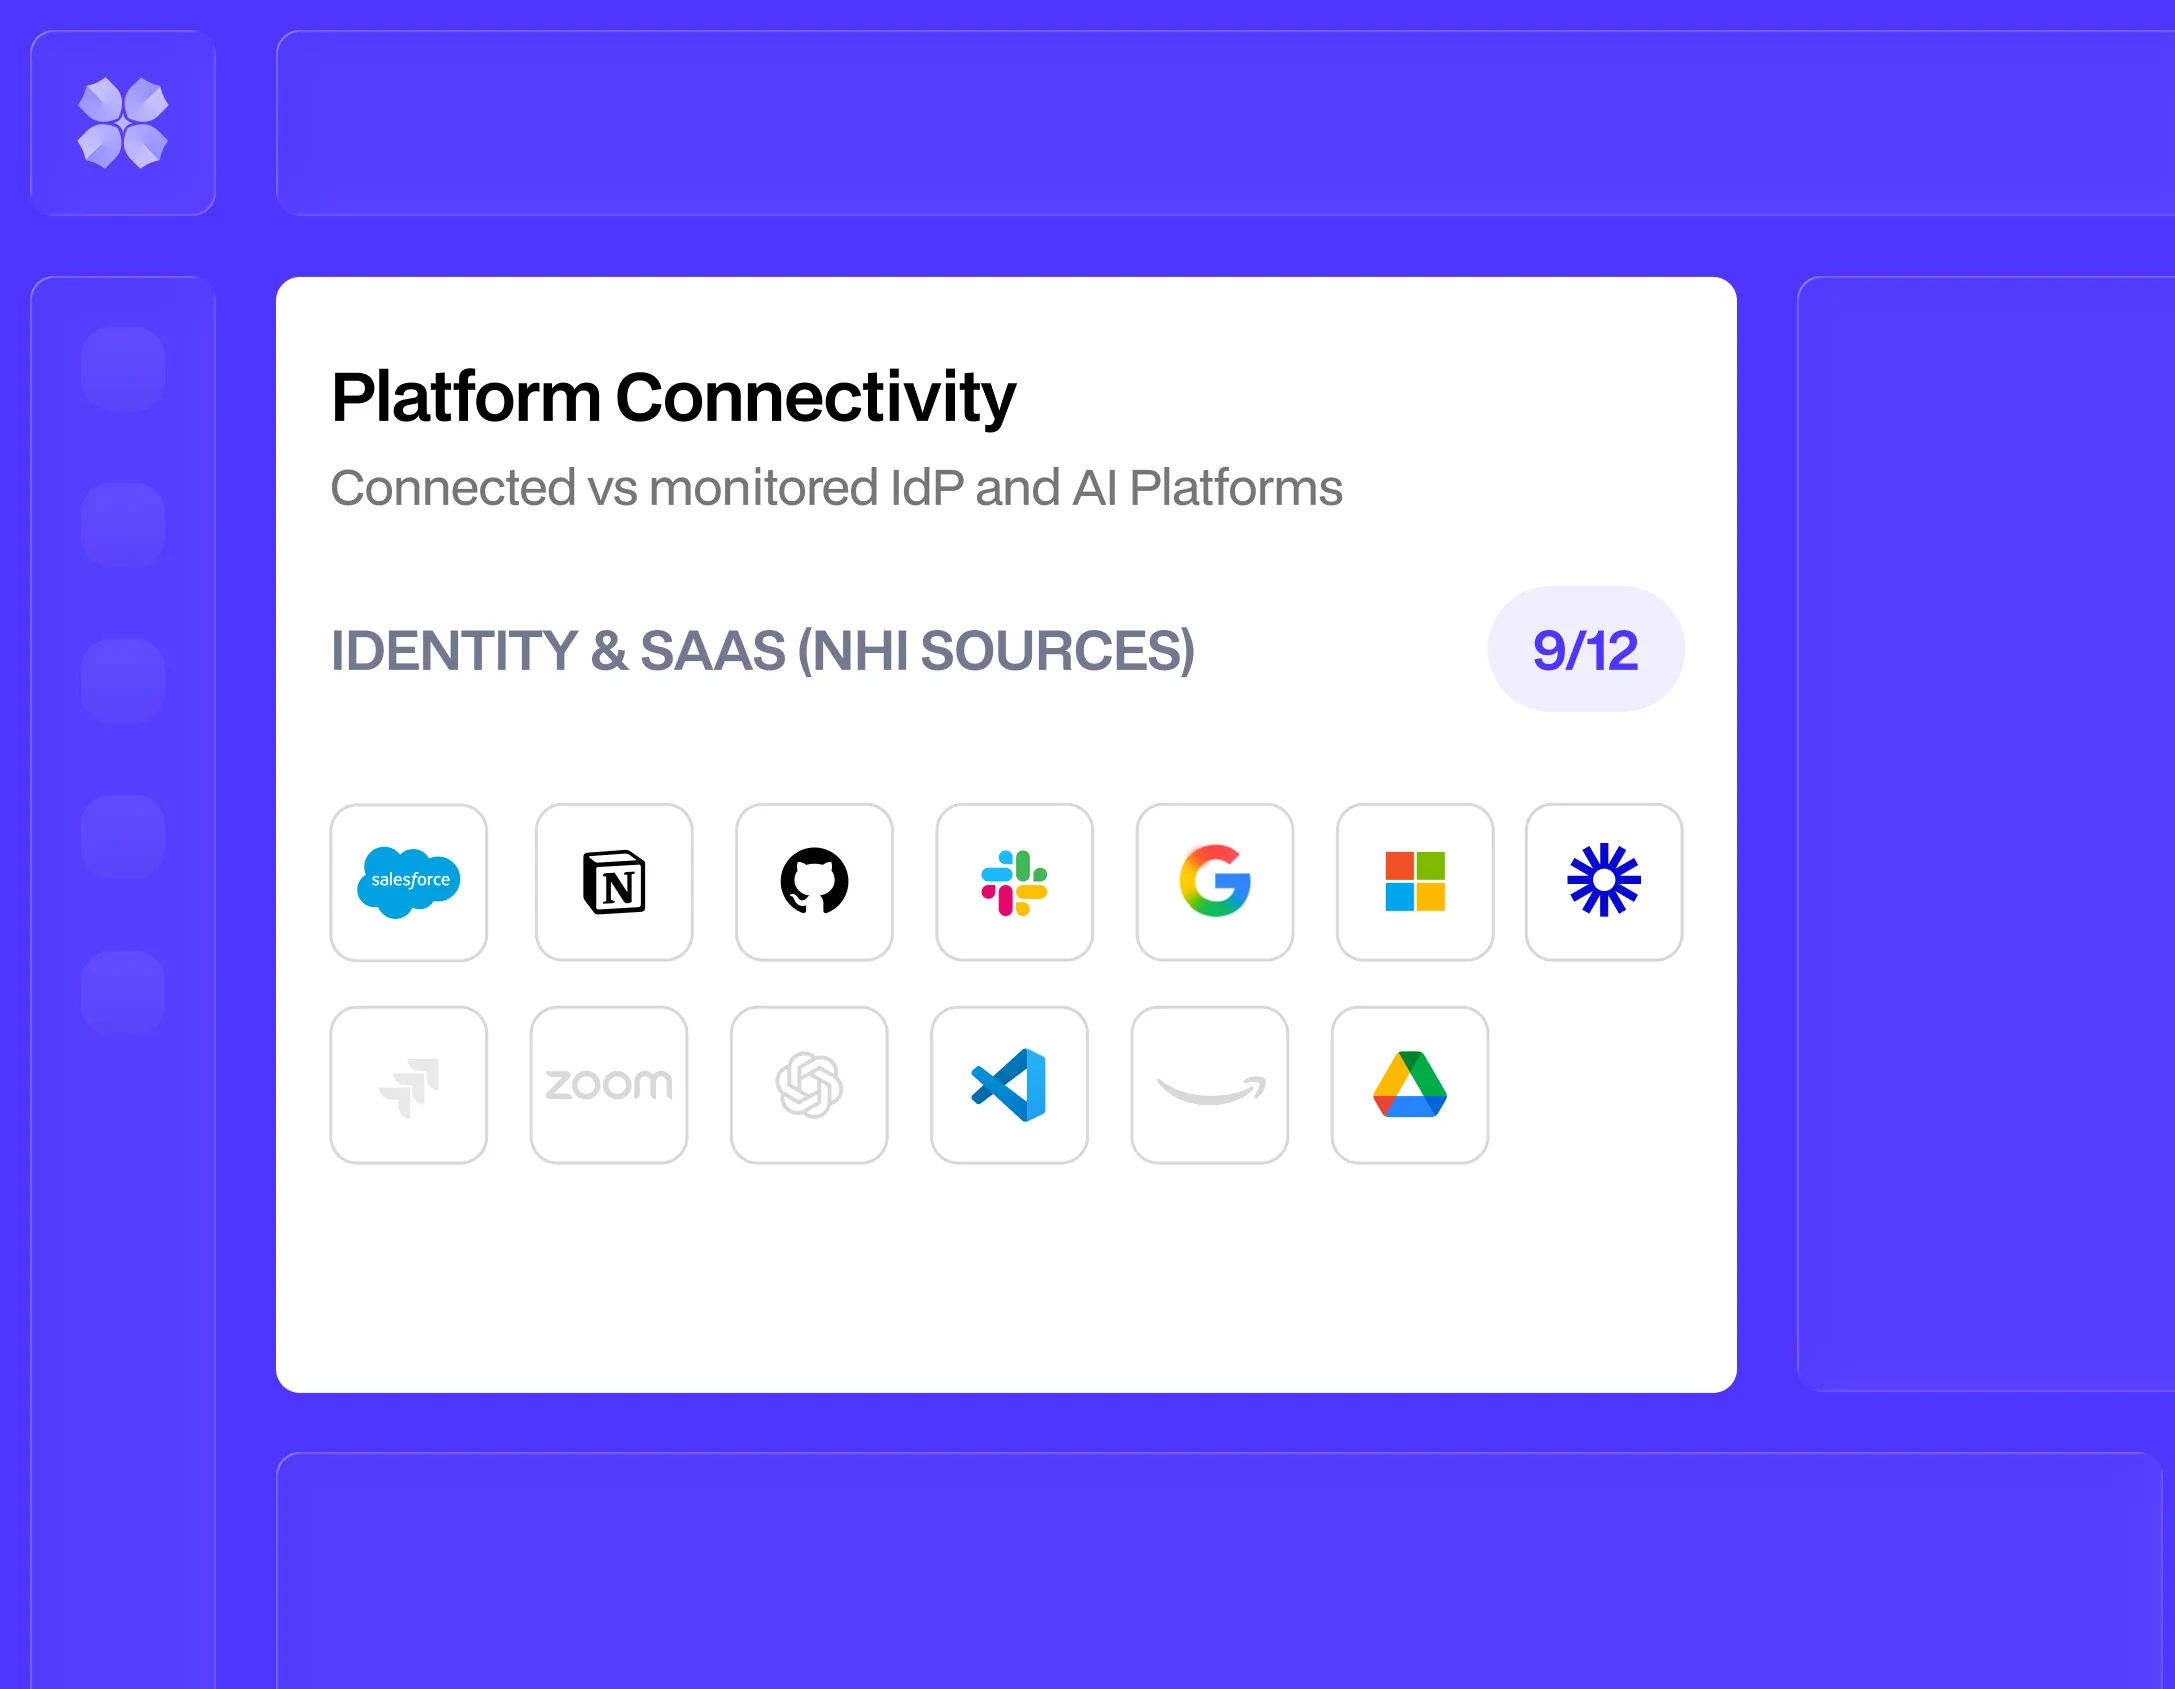
Secure Every Identity Behind Your Automation
Discover non-human access paths, enforce least-privilege policies, and control automated actions with LangProtect.